I wonder if it’s possible to identify the origin of this spam through the data we have. Have you thought about this or looked into it?
I think it’s possible to identify the spammer only if they connected to your node. the pattern which gives them away would be lots of exactly 1 address per ADDR message at an inflated rate.
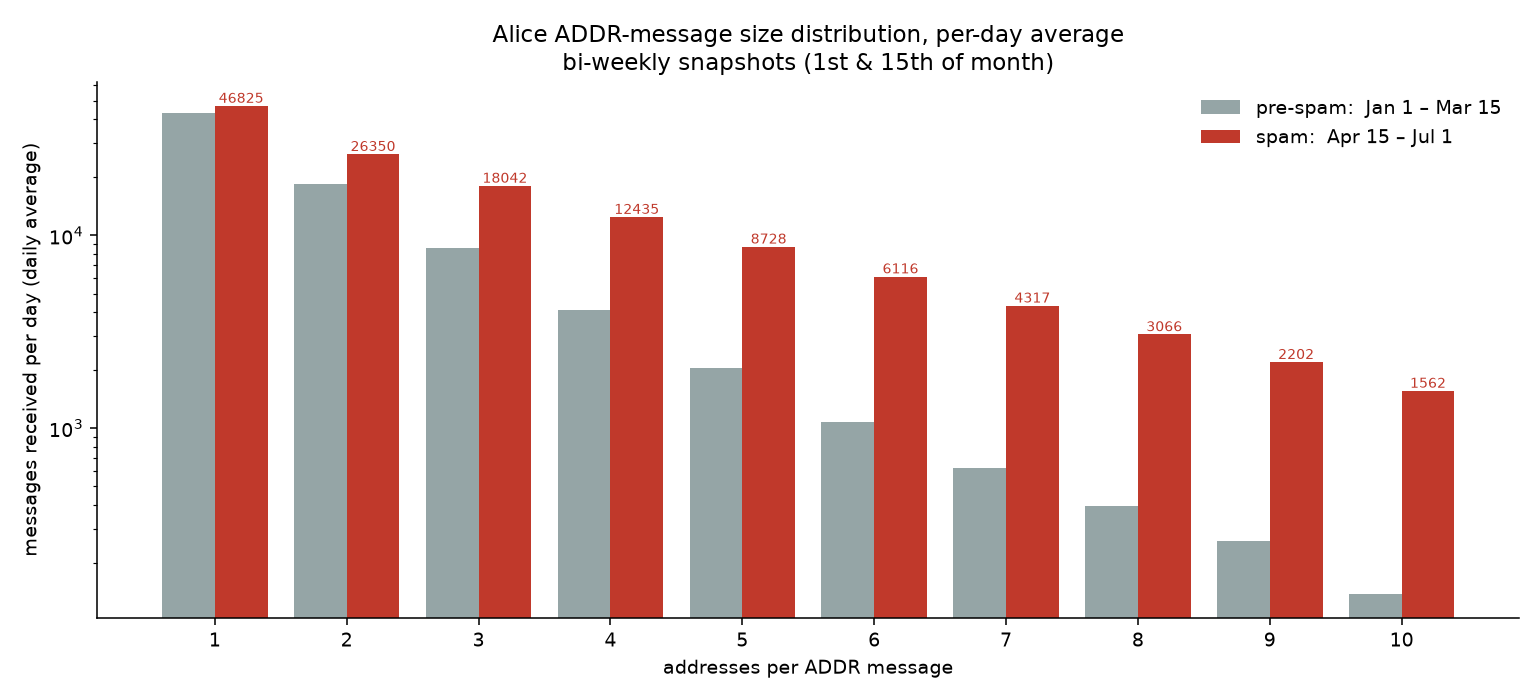
the rest of the network which relays the addresses from the spammer would end up relaying x addresses per ADDR message (x can be 1-10 and would be variable based on the receiving token buckets the normal nodes in the network have). we can see this effect in this graph which shows a sharp increase in all possible number of addresses per ADDR messages.